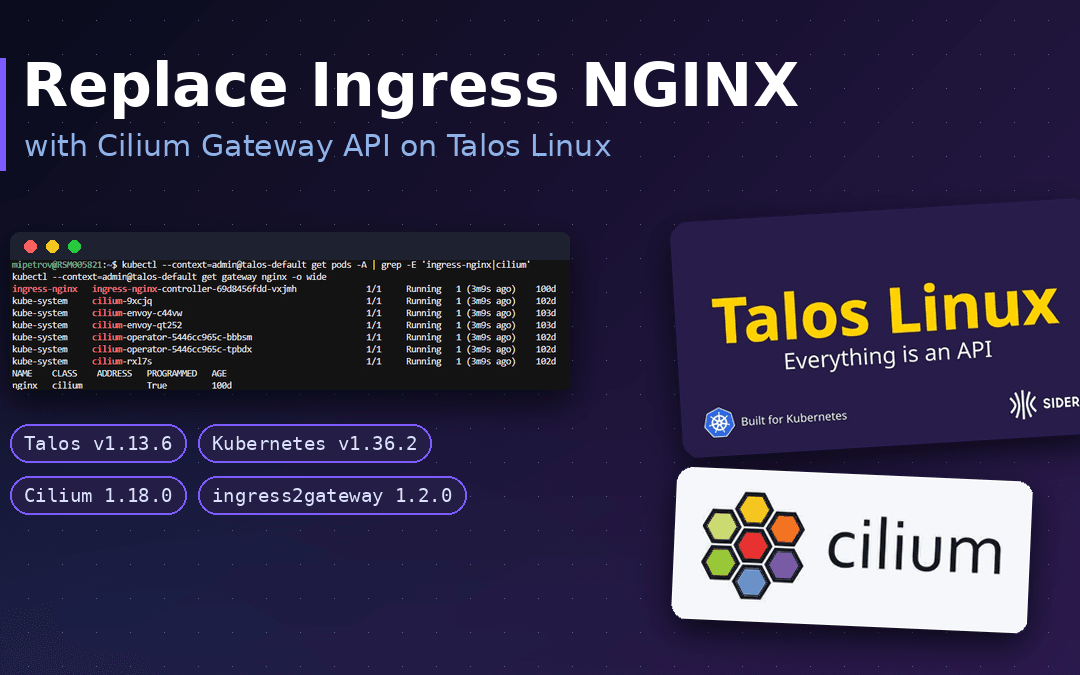
In July 2026 we converted one Ingress on our lab cluster from Ingress NGINX to the Cilium Gateway API, on Talos Linux, using ingress2gateway 1.2.0. This article shows the cluster, the YAML that is still running there today, and why we have not deleted the old controller yet.
It does not repeat the setup. Cilium itself is covered in our guide to install Cilium on Talos, and the CRDs in how to install the Gateway API CRDs.
TL;DR
On 14 July 2026 we ran ingress2gateway 1.2.0 against one Ingress and applied the result to Cilium. The Gateway nginx has been Accepted and Programmed since that day, but it still has no address. Ingress NGINX 1.15.1 is still running beside it, and both objects send demo.example.com to the Service demo-app on port 80. We did not delete the old controller.
The cluster this ran on
| Component | Version |
|---|---|
| Talos | v1.13.6 |
| Kubernetes | v1.36.2 |
| containerd | 2.2.5 |
| Cilium | 1.18.0 |
| ingress-nginx | 1.15.1 (chart 4.15.1) |
| ingress2gateway | 1.2.0 |
One control plane (10.5.0.2) and one worker (10.5.0.3). Both nodes are Talos containers created by the docker provisioner, running on WSL2 with kernel 5.15.167.4-microsoft-standard-WSL2.

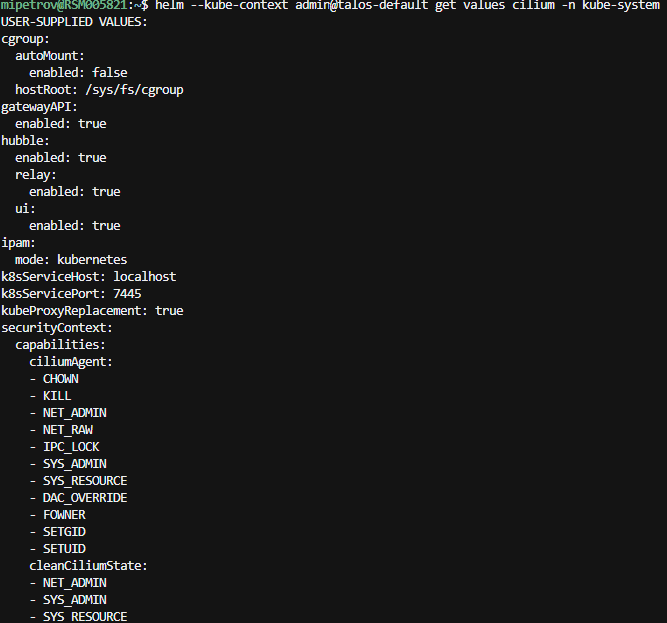
Cilium was already installed with the Gateway API turned on. These are the user-supplied Helm values on the cluster:
helm get values cilium -n kube-systemcgroup:
autoMount:
enabled: false
hostRoot: /sys/fs/cgroup
gatewayAPI:
enabled: true
hubble:
enabled: true
relay:
enabled: true
ui:
enabled: true
ipam:
mode: kubernetes
k8sServiceHost: localhost
k8sServicePort: 7445
kubeProxyReplacement: true
securityContext:
capabilities:
ciliumAgent:
- CHOWN
- KILL
- NET_ADMIN
- NET_RAW
- IPC_LOCK
- SYS_ADMIN
- SYS_RESOURCE
- DAC_OVERRIDE
- FOWNER
- SETGID
- SETUID
cleanCiliumState:
- NET_ADMIN
- SYS_ADMIN
- SYS_RESOURCEk8sServiceHost: localhost with port 7445 is KubePrism, the local API endpoint Talos runs on every node. gatewayAPI.enabled and kubeProxyReplacement were both true before the conversion.
The Ingress we started from
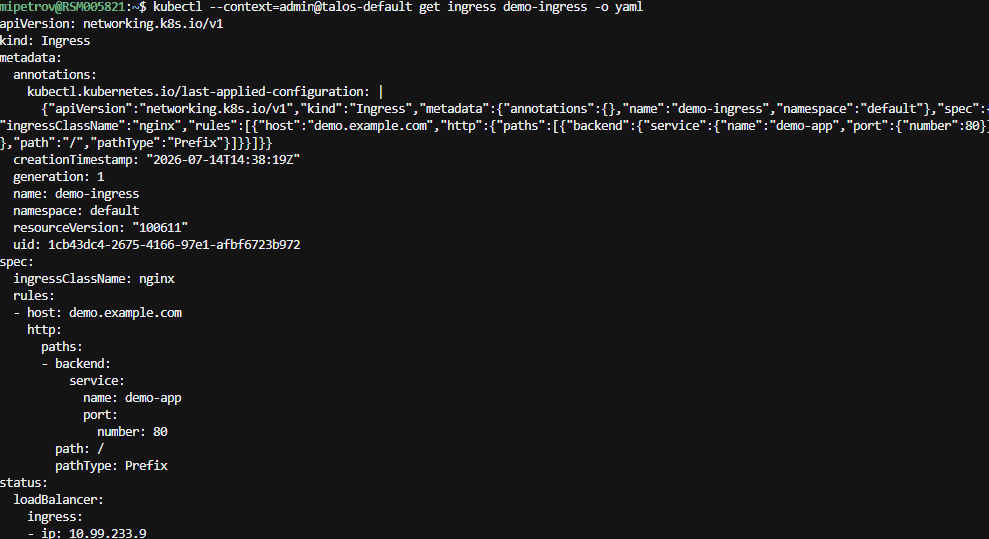
demo-ingress was created at 14:38 UTC on 14 July 2026. This is the object ingress2gateway read:
kubectl apply -f - <<'EOF'
apiVersion: networking.k8s.io/v1
kind: Ingress
metadata:
  name: demo-ingress
  namespace: default
spec:
  ingressClassName: nginx
  rules:
  - host: demo.example.com
    http:
      paths:
      - path: /
        pathType: Prefix
        backend:
          service:
            name: demo-app
            port:
              number: 80
EOF
Its status reports 10.99.233.9. That is the ClusterIP of the ingress-nginx-controller Service, not an external load balancer.
The Gateway and HTTPRoute ingress2gateway wrote
Fifty-five minutes later, at 15:33 UTC, the converted objects were on the cluster. Both carry the annotation gateway.networking.k8s.io/generator: ingress2gateway-1.2.0. The ingress2gateway print command and the gatewayClassName swap are explained in why Ingress NGINX reached end of life. Below is the YAML the apply left behind, without the status and server-side fields.
kubectl apply -f - <<'EOF'
apiVersion: gateway.networking.k8s.io/v1
kind: Gateway
metadata:
  name: nginx
  namespace: default
  annotations:
    gateway.networking.k8s.io/generator: ingress2gateway-1.2.0
spec:
  gatewayClassName: cilium
  listeners:
  - name: demo-example-com-http
    hostname: demo.example.com
    port: 80
    protocol: HTTP
    allowedRoutes:
      namespaces:
        from: Same
EOF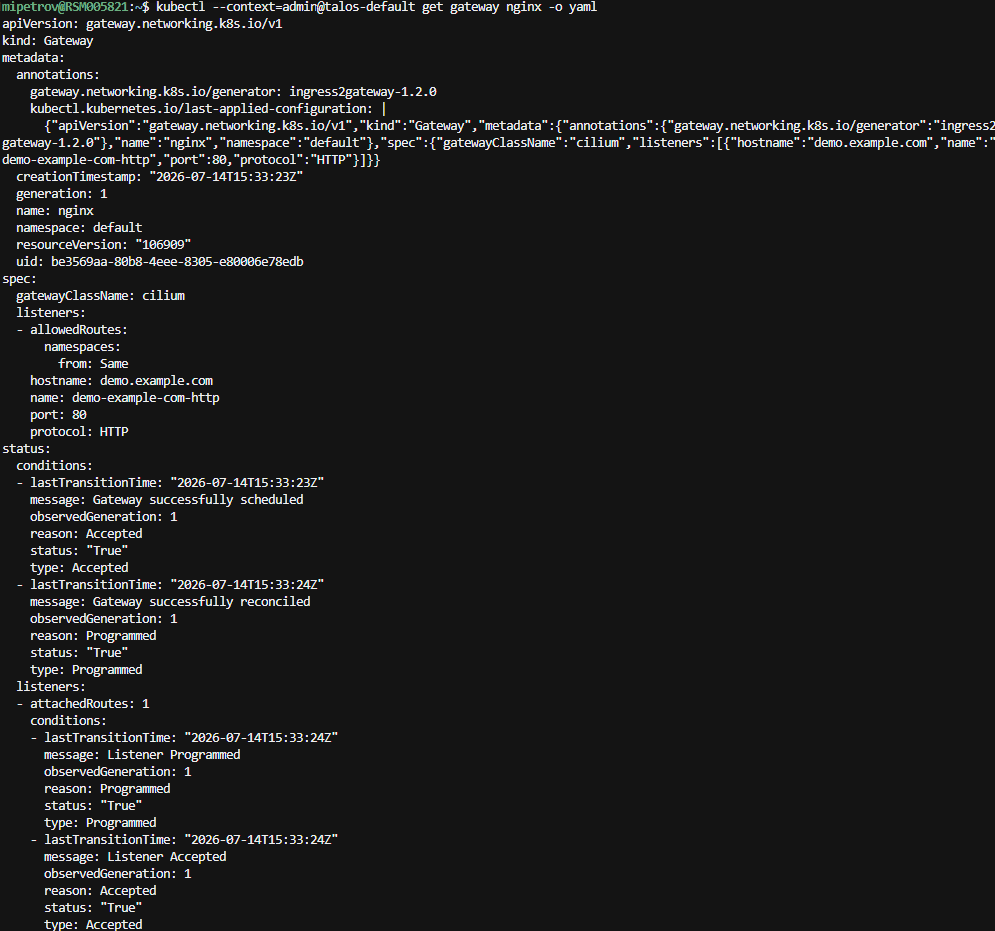
kubectl apply -f - <<'EOF'
apiVersion: gateway.networking.k8s.io/v1
kind: HTTPRoute
metadata:
  name: demo-ingress-demo-example-com
  namespace: default
  annotations:
    gateway.networking.k8s.io/generator: ingress2gateway-1.2.0
spec:
  hostnames:
  - demo.example.com
  parentRefs:
  - group: gateway.networking.k8s.io
    kind: Gateway
    name: nginx
  rules:
  - matches:
    - path:
        type: PathPrefix
        value: /
    backendRefs:
    - name: demo-app
      port: 80
EOF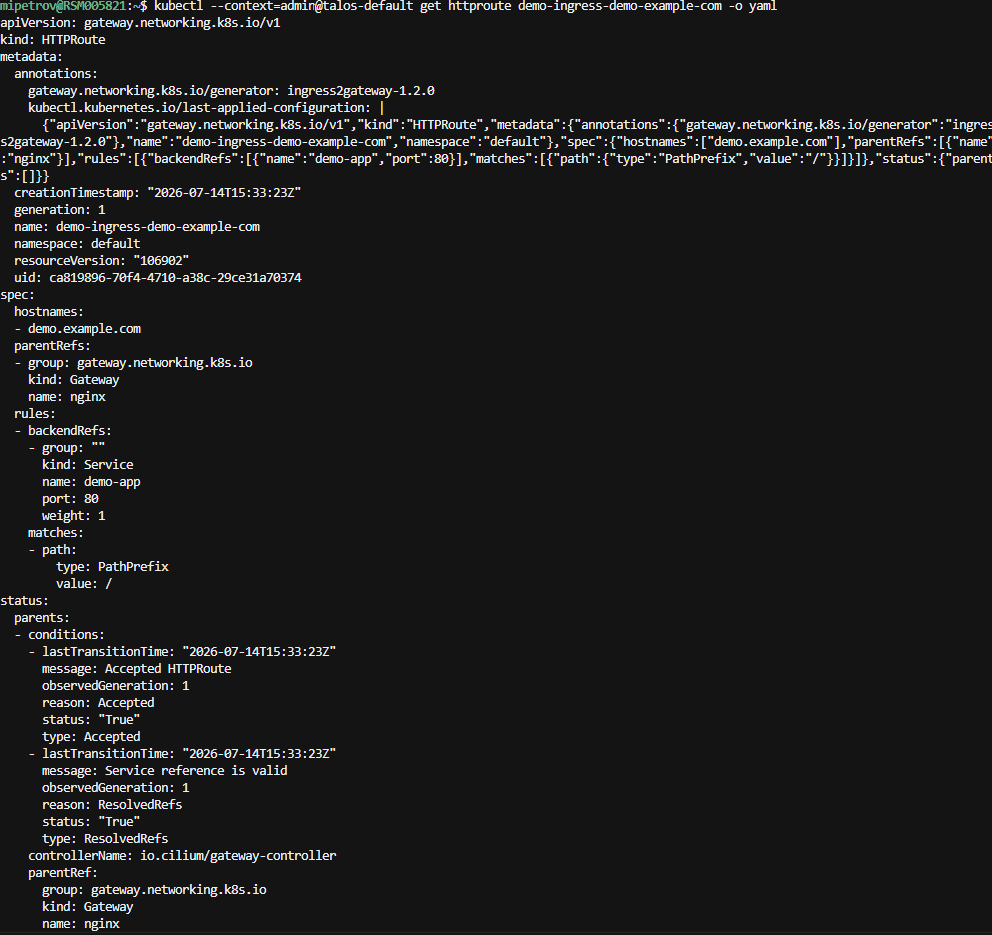
On 22 October 2026 the status is the same as on the day it was created:
- Gateway:
AcceptedandProgrammedare True. - Listener
demo-example-com-http: Programmed, with one attached route. - HTTPRoute:
AcceptedandResolvedRefs, controllerio.cilium/gateway-controller. status.addresseson the Gateway: empty.
Why Ingress NGINX is still there
PROGRAMMED=True means Cilium accepted and configured the Gateway. It does not mean the Gateway has an address. On this docker-based cluster nothing assigns the Gateway an IP, and the ingress-nginx Service is a ClusterIP. If we deleted the controller now, demo.example.com would lose the only address it has.
kubectl get pods -A | grep -E 'ingress-nginx|cilium'
kubectl get gateway nginx -o wide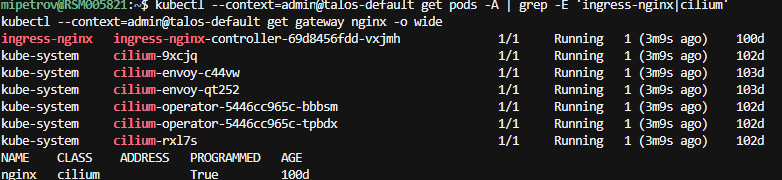
What broke on Talos
The two node containers had been stopped for about three months. When we started them again on 22 October 2026, the Cilium agent on the control plane failed its iptables reconciliation:
iptables v1.8.8 (nf_tables): unknown option "--transparent"
Warning: Extension socket revision 0 not supported, missing kernel module?
The WSL2 kernel does not provide the socket match, so Cilium could not install its transparent-proxy rule. The agent logged that it would retry later. A few minutes after the start, cilium, cilium-envoy, cilium-operator and ingress-nginx-controller were all 1/1 Running. The Gateway conditions did not change: lastTransitionTime is still 2026-07-14T15:33:24Z.
Common mistakes
- Treating
PROGRAMMED=Trueas proof that clients can connect. Checkstatus.addressesas well. - Deleting ingress-nginx while that address list is empty.
- Applying the ingress2gateway output before changing
gatewayClassNametocilium. The tool writesnginxunless you change it. - Reinstalling the CRDs or Cilium for this step. On this cluster that work was already done.
Frequently asked questions
Does the Gateway API replace Ingress?
What replaces ingress-nginx on Talos?
Can Ingress NGINX and a Cilium Gateway run together?
Conclusion
ingress2gateway 1.2.0 produced a Gateway and an HTTPRoute that Cilium has kept Programmed for a hundred days. The cutover stops there until the Gateway has an address. Until then, the Ingress stays.
Official references: the Cilium Gateway API documentation, the ingress2gateway repository, and the Ingress NGINX retirement announcement.