On 22 October 2026, the day after the PHP2Shell fix shipped, our Laravel app was still running a vulnerable PHP. The Dockerfile said php:8.4-fpm, and that tag already pointed at the fixed release. The image in production had been built a month earlier. This is how we found it, pinned it, rebuilt it through GitHub Actions, and what broke on the way.
TL;DR
Our image was built on 22 September from the floating php:8.4-fpm tag. A tag only matters at build time, so the running container had no fix. We pinned the base to php:8.4.27-fpm, made CI pull a fresh base on every build, and redeployed. Staging deployed on its own. Production built the image and then failed at the SSH login, so we deployed it by hand. Both now report PHP 8.4.27, and a day later production moved to an SSH key too.
What PHP2Shell is
PHP2Shell is two bugs in PHP itself, CVE-2026-109618 and CVE-2026-109619, both rated CVSS 9.2. They allow remote code execution without authentication on any PHP that serves web requests, including PHP-FPM. The fixed releases are 8.5.12, 8.4.27, 8.3.36 and 8.2.35. PHP 8.1 and older get no upstream fix. Updating Laravel does nothing here: the bug is in the runtime, not the framework.
The setup this ran on
| Staging | Production | |
|---|---|---|
| App | Laravel 12.15.0 | Laravel 12.15.0 |
| Runtime | php:8.4-fpm, multi-stage | php:8.4-fpm, multi-stage |
| Registry | GHCR | GHCR |
| Deploy | GitHub Actions on develop | GitHub Actions on main |
Each push builds the image and pushes it to GHCR. The workflow then logs in to the server over SSH, pulls the image, and recreates the containers.
Step 1 — Check what PHP the container actually runs
Do not read the Dockerfile. Ask the running container:
C=$(docker ps --format '{{.Names}}' | grep -E -- '-app$')
docker exec "$C" php -v | head -1
docker exec "$C" php-fpm -v | head -1
docker inspect -f 'container started {{.State.StartedAt}}' "$C"
docker image inspect -f 'image created {{.Created}}' "$(docker inspect -f '{{.Image}}' "$C")"
Check both binaries. The CLI and FPM come from the same build, but FPM is the process that faces the internet.
Why php:8.4-fpm did not patch us
php:8.4-fpm has pointed at 8.4.27 since 21 October. Our image was built on 22 September, and a tag only matters at build time. Until something rebuilds the image and pulls the base again, the container keeps the PHP it was built with. With cache-from: type=gha, even a rebuild can reuse the old base layer.
Step 2 — Pin the base image
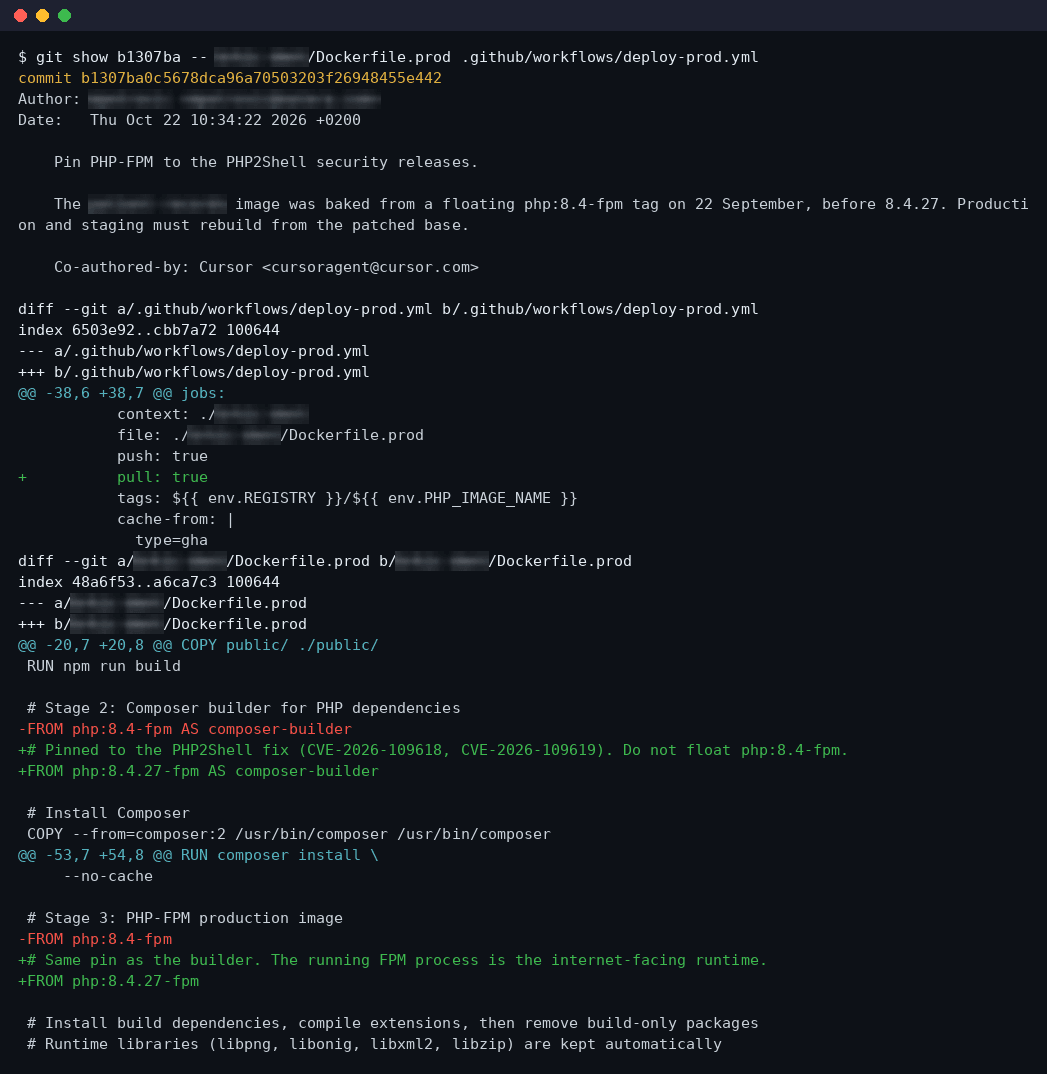
Both stages of Dockerfile.prod, the Composer builder and the runtime, moved to the exact patched tag:
# Stage 2: Composer builder for PHP dependencies
# Pinned to the PHP2Shell fix (CVE-2026-109618, CVE-2026-109619). Do not float php:8.4-fpm.
FROM php:8.4.27-fpm AS composer-builder

# Stage 3: PHP-FPM production image
# Same pin as the builder. The running FPM process is the internet-facing runtime.
FROM php:8.4.27-fpm
The local development Dockerfile got the same treatment on its own branch: php:8.2-fpm became php:8.2.35-fpm.
Step 3 — Force a fresh base in CI
One line in the docker/build-push-action step of both workflows:
context: ./<app>
          file: ./<app>/Dockerfile.prod
          push: true
          pull: true
pull: true makes BuildKit fetch the base image from the registry on every build instead of trusting the layer cache. Both changes went into a single commit:
Step 4 — Deploy, and what broke
The commit landed at 10:34 on 22 October, on develop and, through a merge, on main. Staging deployed by itself in 5 minutes 14 seconds. Production ran for 4 minutes 27 seconds and went red.
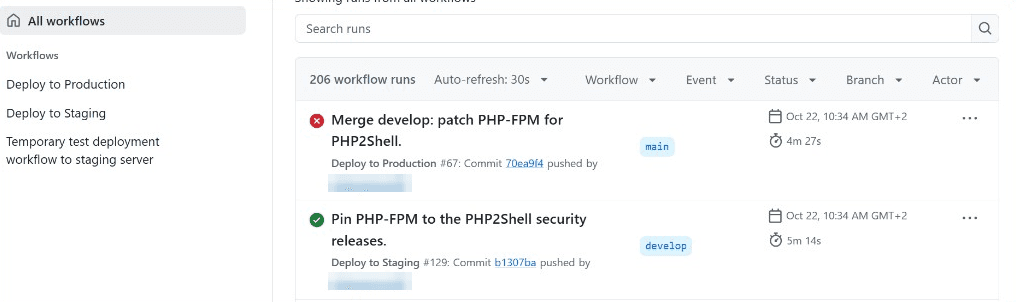
The build and push step on production passed. The SSH step did not. The workflow still logged in with a password secret, and the server accepts keys only:
ssh: handshake failed: ssh: unable to authenticate, attempted methods [none], no supported methods remain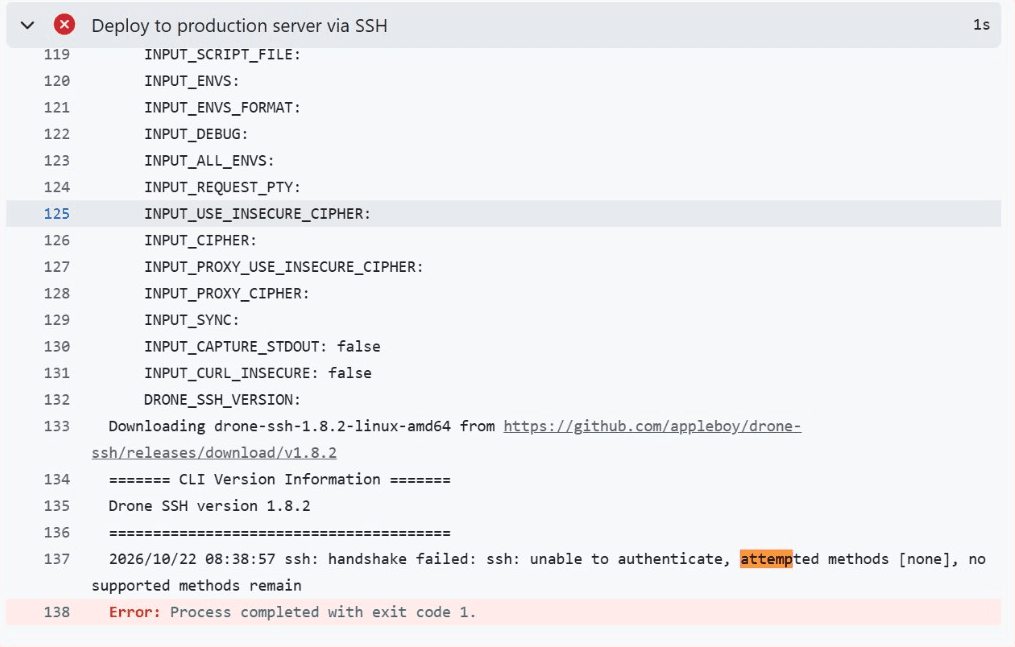
Staging had switched its deploy to an SSH key on 9 October. Production had not. We ran the same steps the workflow runs, by hand, with the key:
docker pull ghcr.io/<owner>/<app>:production
docker pull ghcr.io/<owner>/<app>-nginx:production
docker compose -f docker-compose.prod.yml up -d --force-recreate --no-deps <app> <app>-nginx
docker logout ghcr.io
The production container started at 10:44, six minutes after the failed job.
On 23 October production switched its deploy to an SSH key as well, the same change staging got on 9 October. The next run, Deploy to Production #68, went green.
Verify
Output from the staging container on 23 October:



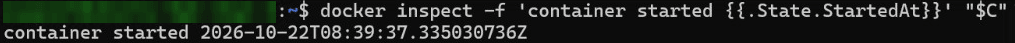
Production returned the same PHP and Laravel versions:
| Image created | Container started | |
|---|---|---|
| Staging | 2026-10-22 10:37 | 2026-10-22 10:39 |
| Production | 2026-10-22 10:37 | 2026-10-22 10:44 |
The DevSecOps checklist we use now
This patch was a small change. Most of the work was in the pipeline around it. That is the line between DevOps and DevSecOps we describe in DevOps vs DevSecOps.
Done on this pipeline:
- Base image pinned to the exact patched tag, in every stage.
pull: truein CI, so a warm cache cannot hide an old base.- Verification inside the running container, not in the Dockerfile.
- A failed deploy treated as a failed patch, even when the build was green.
- Staging and production deploy over an SSH key. After the manual production deploy,
docker logoutremoved the registry login from the server.
Next steps, not done yet:
- Scan the image in CI and fail the build on critical CVEs. We will cover that with Trivy in a follow-up article.
- Get an automatic pull request when a new patched base image is released, so the pin does not go stale.
Common mistakes
- Reading
FROM php:8.4-fpmand assuming you are patched. - Rebuilding with a warm cache and no
pull: true. - Checking
php -von the host instead of inside the container. - Trusting a green build. On production the build passed and the deploy failed.
- Leaving a deploy secret on an auth method the server no longer allows.
Frequently asked questions
Do I need to update Laravel for PHP2Shell?
Is php:8.4-fpm patched now?
Which PHP versions fix PHP2Shell?
Conclusion
The patch was one line per stage. The real work was proving the running container had it, and noticing that a green build did not mean a deploy. If your CI still logs in with a password, move it to a key. For us it was one commit. It is the same pipeline discipline we describe in what a DevOps pipeline is.
Official references: the PHP security release, the PHP Foundation write-up, and CERT/CC VU#763488.